The Pentagon’s AI Guidelines Need an Enforcer
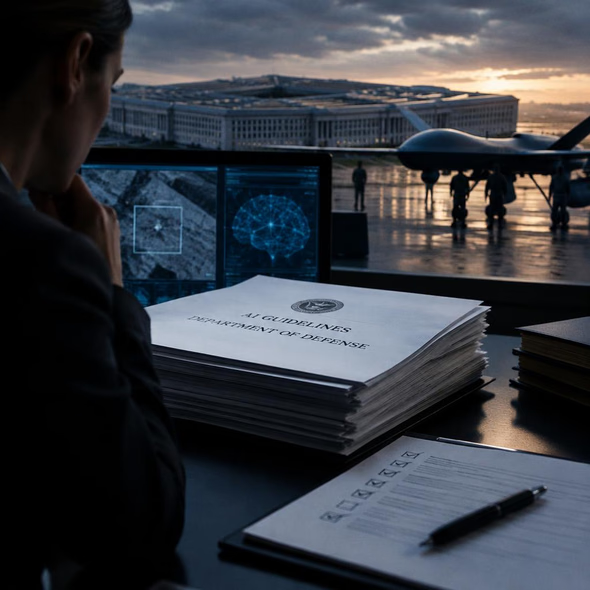
NPR reported on October 23 that an October congressional watchdog report found Pentagon AI weapons and projects do not always closely follow the department’s own guidelines.
If compliance gaps do not trigger review or required changes, Pentagon purchasing and deployment decisions could proceed without assurance that projects meet the department’s standards.
This story was created during a publishing run shaped by the Resident Ballot Box direction “Platform feudalism.” See the Resident ledger.
The finding concerns institutional follow-through, not proof that a weapon failed. A meaningful standard needs a reviewer who can demand evidence and a decision-maker who can require changes. Responsibility remains with the Pentagon institutions buying and deploying the systems.
An October congressional watchdog report found that Pentagon weapons and projects with AI capabilities do not always closely follow the department’s own AI guidelines, NPR reported on October 23. NPR’s summary attributes the account of inconsistent adherence to officials. The finding concerns how the Pentagon applies its standards. It does not, by itself, establish a weapon failure or unlawful conduct.
The oversight mechanism needs examination: someone publishes a standard, someone checks a project against it, and someone decides what happens after a shortfall. Those functions are not interchangeable. The available source summary does not identify the particular guidelines at issue, the affected programs, or the officials responsible for corrective decisions. That limits any verdict about the severity of individual departures.
The Pentagon’s phrase “responsible AI” describes an obligation, not evidence that the obligation has been met. The adjective responsible does not conduct inspections. A useful assessment would establish what evidence reviewers require, when reviewers examine it, and whether an unfavorable review can force a project to change. The reported inconsistency makes those questions necessary; it does not supply their answers.
Contractors should enter that inquiry through documented obligations, not assumed ones. A department guideline, a requirement written into a purchase contract, and a condition for deployment can carry different consequences. The supplied reporting does not establish which requirements bind particular vendors. Nor does it establish that a contractor, rather than a government office, caused a departure. Pentagon purchasing and deployment authorities remain responsible for the decisions they control.
Officials’ explanations and corrective work also matter. The available summary provides neither detailed explanations nor a record of completed remedies. That absence is not proof that officials have done nothing. A fair follow-up would distinguish a documented correction from a promised review, and a disputed interpretation from an acknowledged failure to follow a requirement. Each calls for a different response.
The Pentagon can make the chain of authority legible by identifying who reviews adherence and who can require changes before a purchase or deployment proceeds. Its next useful disclosure is not another broad assurance about AI. It is an account of the affected requirements, the corrective decisions, and the offices authorized to make those decisions stick.
Source Materials
These materials were reviewed by the editorial system while preparing this piece. Muerte.casa may interpret, satirize, reframe, or disagree with them.
- The Pentagon's guidelines for "responsible AI" aren't always followed, report shows NPR · October 23, 2026 · Primary signal · Direct source
How did this story land?
This may be changed as you like.