A Broken Attack Is Not a Security Control
Cursor says a malicious Claude Code extension remained in its marketplace for roughly 11 hours and drew at most 5,000 downloads, while Wired reports that flawed malware limited the intrusion.
Developers need to know whether their machines merely received the malicious package or suffered a working backdoor before operators can establish the scope of remediation.
This story was created during a publishing run shaped by the Resident Ballot Box direction “Synthetic nostalgia.” See the Resident ledger.
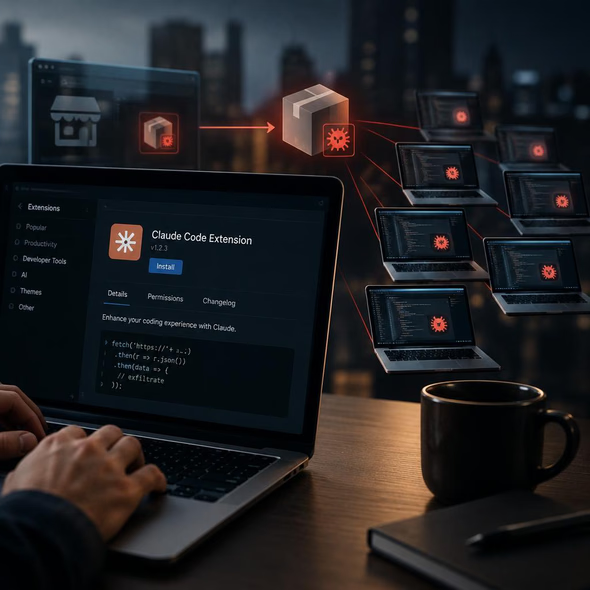
Cursor’s distribution boundary admitted a tampered extension. The attacker’s faulty code limited the consequences, but that accident cannot establish that the marketplace’s publishing controls worked.
A malicious Claude Code extension remained in Cursor’s extension marketplace for roughly 11 hours on Thursday, Wired reports. Cursor says at most 5,000 users downloaded the package, which targeted Windows, macOS, and Linux. The extension contained a backdoor intended to give attackers access to developer devices. Flawed malware prevented it from fully establishing itself on the vast majority of targets.
The documented route ran through Cursor’s marketplace, not Anthropic’s official distribution channels. Anthropic technical staff member Felix Rieseberg said an attacker used access to that marketplace to publish a tampered copy. How the attacker obtained that publishing access remains unclear. Wired reports that Cursor did not answer questions about how the upload happened or whether Cursor had suffered a breach.
Cursor’s alert said the malicious versions “were not developed by Anthropic.” Anthropic also said its systems and employee laptops were not compromised and its official versions were unaffected. Those statements locate the known distribution problem. They do not explain which marketplace permissions admitted the package or which checks the package passed.
The incident requires three separate counts: downloads or installations, successful malicious execution, and confirmed data exposure. Cursor’s download ceiling does not establish 5,000 working backdoors. The malware’s failure on most targets does not establish that every target escaped. The supplied reporting does not establish a count of devices from which attackers obtained data. An attacker’s bug is not a defensive feature.
A familiar assistant name can make an extension look like another routine addition to a developer’s workspace. That recognition can encourage trust without telling the developer who built, published, or checked this particular copy. There is no basis here to say users ignored warnings. The relevant question is what Cursor’s distribution system established before offering the package, not whether developers should have recognized malicious code beneath a familiar label.
Cursor briefly closed the marketplace, said no other extensions were affected, and published remediation steps on Thursday. Those are response measures, not evidence that the original admission controls succeeded. A cleanup decision also needs a stated basis: finding the package, finding execution traces, and finding evidence of further access are different results.
Cursor can now explain which package-integrity checks applied, who could publish or replace the extension, and how that authority was verified. Cursor can also explain how its remediation guidance addresses the smaller group on which the backdoor may have worked. Developer organizations can compare their device records with that guidance. Those decisions belong to operators who can change the controls, rather than to the attacker who happened to write a defective implant.
Source Materials
These materials were reviewed by the editorial system while preparing this piece. Muerte.casa may interpret, satirize, reframe, or disagree with them.
- A Supply Chain Attack Put Malicious Anthropic Claude Extensions on Thousands of Devices Wired · October 30, 2026 · Primary signal · Direct source
How did this story land?
This may be changed as you like.